Quick brief
Build one coherent decision path from source-qualified records and effective-time history through permission-aware retrieval to a destination that enforces its action conditions. Reuse or federate that path only after duplicate updates, conflicting facts, revoked authority, races and uncertain transaction outcomes have observable handling and accountable owners.
Listen to the AI-generated overview · about 2 minutes
Read the audio transcript
Timestamps are approximate.
0:00
This is the brief on Enterprise Digital Twin implementation. Please note, this is an AI-generated narration for a short overview of Ajith Vallath Prabhakar’s article, “Enterprise Digital Twin implementation: build around one real decision.” It guides us in building a coherent decision path using a fictional purchasing example, organizing records and enforcing rules without overcomplicating the architecture. So, what evidence actually needs to be in place before a system creates an order?
0:27
First, define the decision, the responsible person, and the facts. Take a strictly fictional example: a $48,000 order hitting a former $50,000 limit, an expired delegation, and an active supplier hold. Viewing, recommending, approving, and creating orders all need totally different permissions. The app must check the requester, rules, grants, holds, and budgets, pinpointing exact sources. Missing evidence means asking for a review—never default to yes. A past order doesn’t authorize a new one.
0:56
Second: how do we query this context without letting the interface bypass security? Choose relational or graph queries based on real workloads. Graph storage isn’t mandatory. While MCP exposes bounded lookups, it absolutely does not replace business rules or grant approval. The purchasing system still enforces conditions. Prior lookups aren’t guarantees, so uncertain results require a recovery path.
1:17
Finally, how do you organize these questions without getting stuck in a rigid build order? Just use the five context layers to organize questions, not prescribe an order. Start with a read-only workflow and expand only when ready. Federation is useful only when decisions need outside info; it isn’t mandatory.
1:33
Ultimately, the practical test of your implementation is simple: can a responsible person see exactly why a request is blocked, which evidence supports that result, and who can resolve the remaining issue?
Full analysis
Revised October 18, 2026.
Before building a graph of the organization, write down the decision it needs to support, including the action, responsible person and facts that could change the outcome. Then specify what happens when those facts are missing. This small piece of design work exposes dependencies that can remain invisible in an impressive architecture diagram.
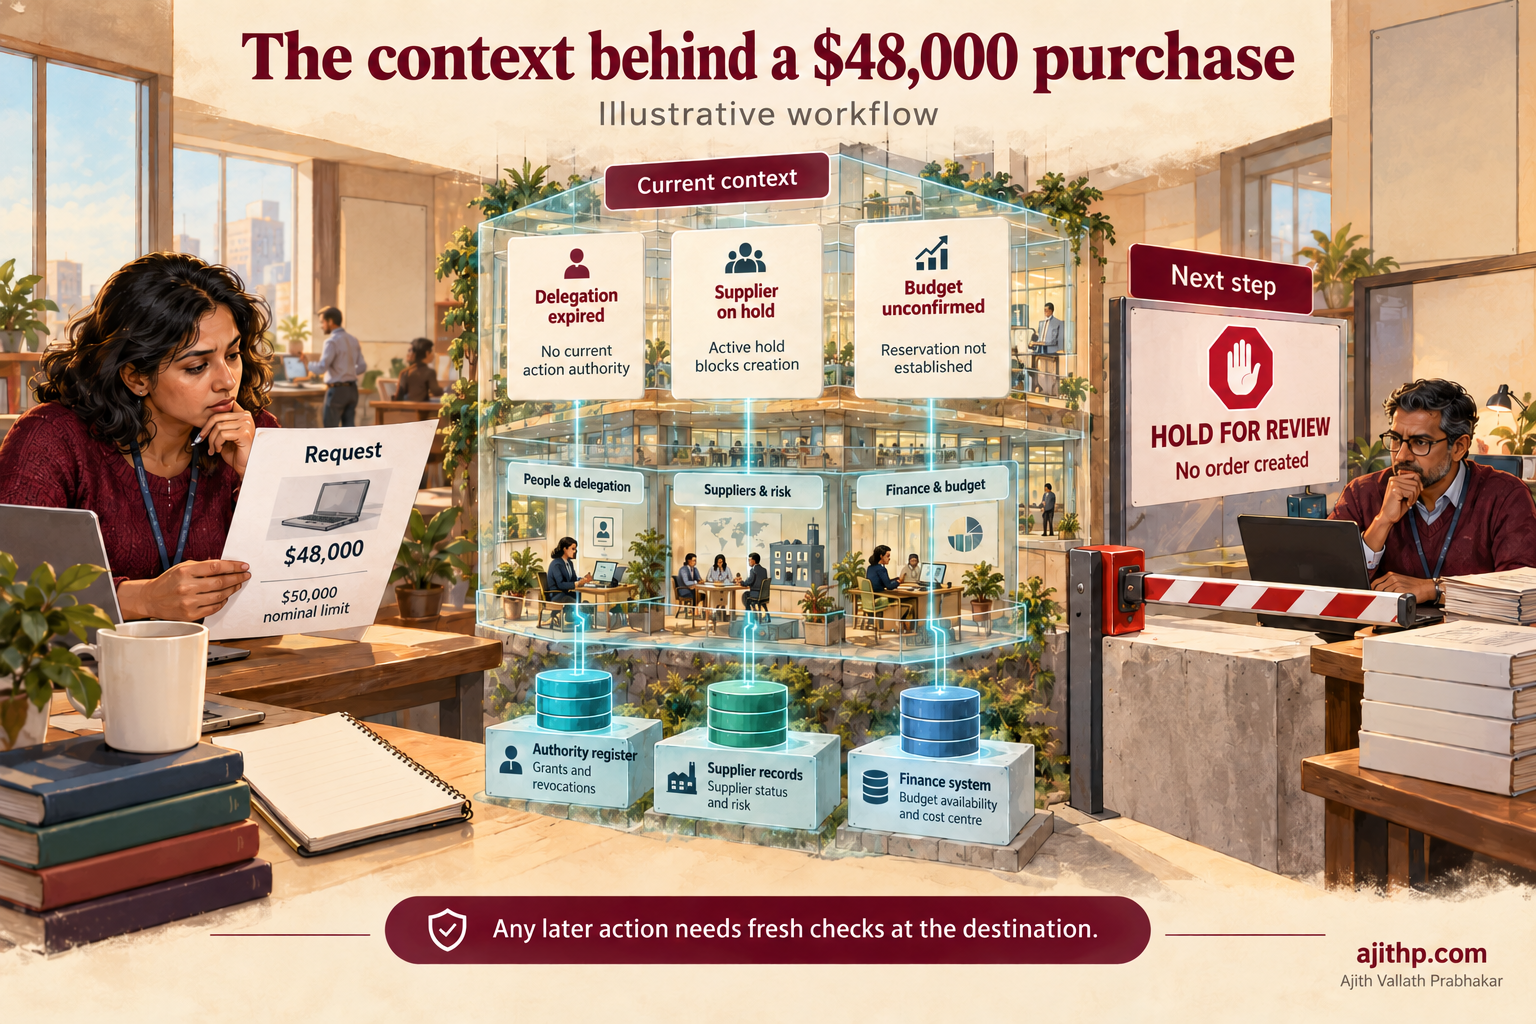
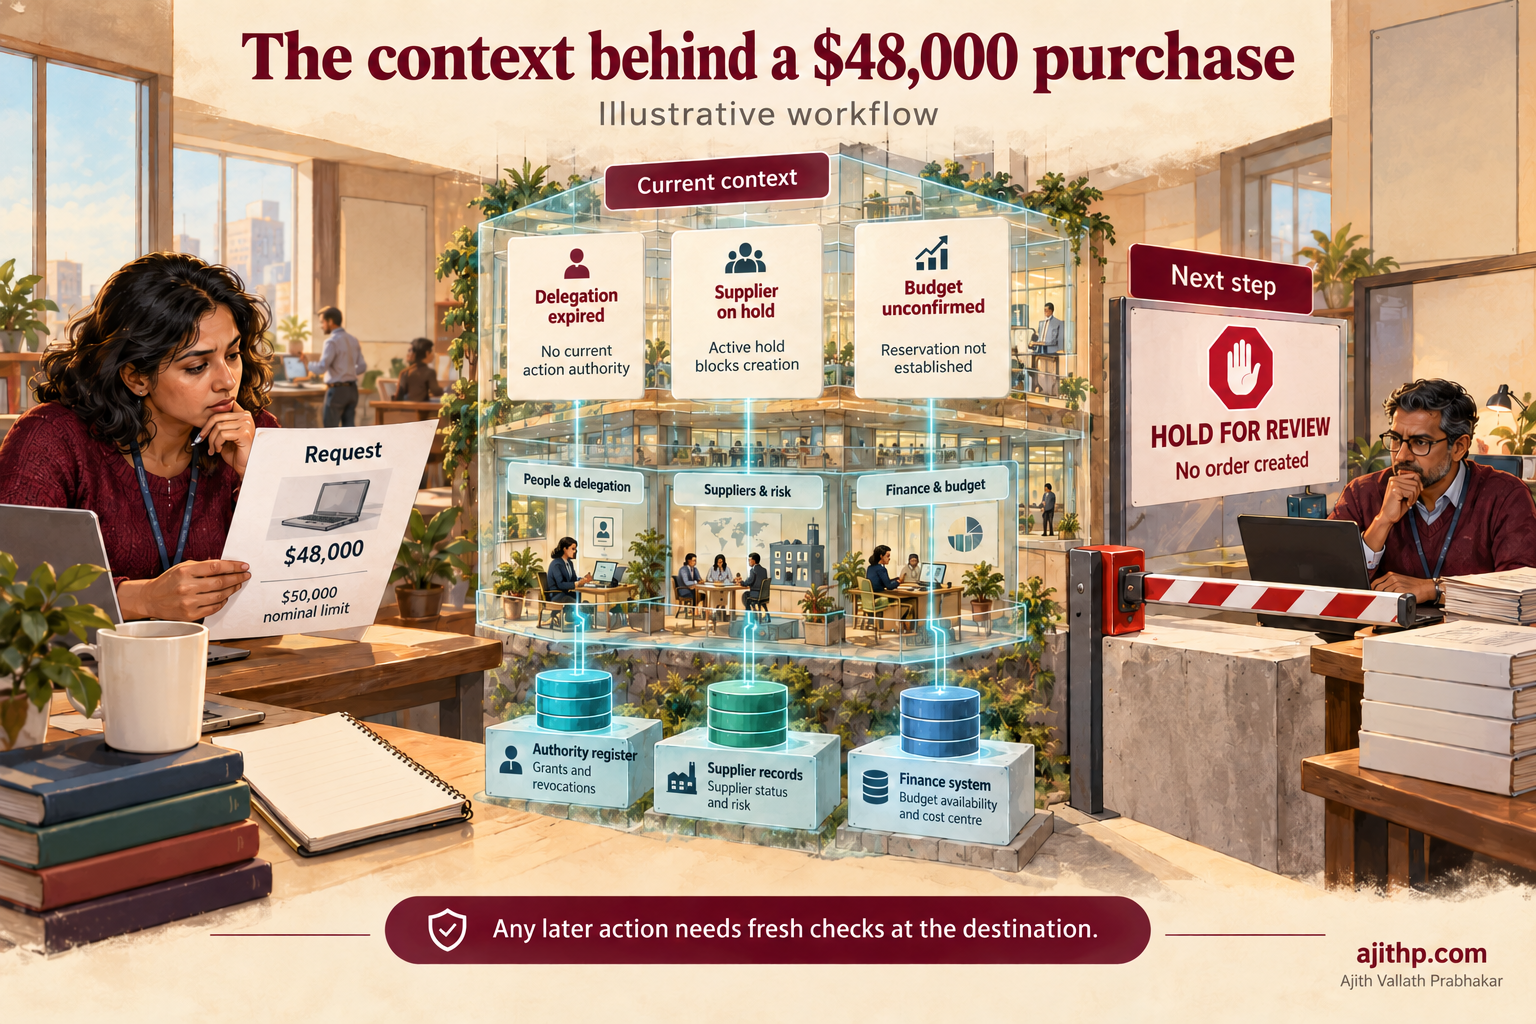
The first article in this series uses an illustrative purchasing request: a $48,000 order, a former $50,000 approval limit, an expired delegation, and an active supplier hold. This guide develops that example into an implementation design. The records and identifiers below are fictional; the response formats describe this application rather than an MCP standard.
The useful next step may be an explanation or a handoff to the current approver. Creating the order belongs later, after the destination system has checked the conditions required for that action. The design needs to make that distinction clear to the person using it and to the software handling the request.
Download the fillable orchestration workbook.
Define a decision context contract
A context contract is a short agreement about the evidence a workflow needs, who owns it, and how the system behaves when it cannot establish the answer. It gives the application team and business owner something concrete to review together.
For the purchasing case, the decision is whether this order can proceed to creation now. The contract should distinguish viewing an order, recommending an approver, obtaining approval, and creating the order. Those are different operations, with different permissions and failure consequences.
| Contract item | Illustrative requirement |
|---|---|
| Intended action | Create purchase order example-po-014 for USD 48,000. |
| Acting identity | Establish the authenticated requester and any delegated service identity. |
| Applicable rule | Resolve the policy for the legal entity and spending category. |
| Current authority | Check a grant whose scope covers the order and whose validity includes the action time. |
| Current state | Check the supplier hold and relevant budget reservations. |
| Missing or conflicting evidence | Return a review requirement; do not silently choose the more permissive record. |
| Execution control | The purchasing system enforces its own action conditions. |
| Outcome evidence | Record the destination’s result and reconcile uncertain attempts. |
Give each requirement an owner. A purchasing-policy owner can define the rule; an identity or delegation owner can establish the source of a grant; the application owner must explain which checks happen when an order is created. A project team should not fill these gaps by putting its own interpretation into a prompt.
Map the five layers to sources you can maintain
The five-layer model organizes the context problem around facts the workflow needs. Because several layers may already be served by the same business application, introducing a separate product for each would often create unnecessary synchronization work. Begin with the systems that own the facts and assess the interfaces they can supply.
Organizational topology needs more than a person’s job title. Represent the role and, when relevant, the explicit grant or delegation that permits an operation within a scope and period. Reporting to a manager does not establish that the manager can authorize every action involving that employee.
This conceptual notation separates those responsibilities. It describes a possible data model, not executable database syntax:
Person --HOLDS--> Role
Person --RECEIVES--> AuthorityGrant
AuthorityGrant --APPLIES_TO--> ActionScope
AuthorityGrant: source, scope, limit, valid_from, valid_to
Policy fabric needs applicability as well as versioning. Retain the issuing owner, effective period, covered entity or region, spending category, and any approved exception. Where an application already implements the purchasing rule, use its supported interface instead of reconstructing a competing rule engine from policy prose.
Operational state needs a source-specific freshness rule. A supplier hold may require a check at execution, while descriptive supplier information can tolerate a longer refresh interval. Budget availability may also depend on reservations made by other workflows. An extracted balance without those reservations can be the wrong input even if it was copied recently.
Institutional memory should retain decision context and outcomes at an appropriate level of detail. Link the earlier request, the reason for an exception, its approving authority, and what happened. A similar prior order can help a reviewer, but the new order still requires its own applicable authority and conditions. Apply access, correction, and retention rules to the history rather than treating it as an unrestricted store of everything people have said.
Constraint topology covers dependencies and practical limits that affect the next step. For this order, supplier review must be completed before creation. In another workflow, a dependency might be a completed legal review or available delivery capacity. Record whether a condition is a hard block, a warning, or something a named role can resolve; those distinctions must survive retrieval and presentation.
An organization may already have most of these facts in relational systems and business applications. The integration problem is then to preserve their meaning, identity, and currentness across the workflow. Copying them into a graph is a storage choice, not proof that the integration problem has been solved.
Give the five layers a coherent minimum model
Identifiers need to survive a display-name change and remain unambiguous across sources. Two applications can both use 1234 while referring to different suppliers, so the identifier must carry its source or an established cross-system identity. Retain the mapping decision and its owner instead of merging records because their names look similar.
The following is a conceptual schema for the purchasing example. It is not a standard ontology or executable database definition. The common evidence fields make it possible to trace each assertion back to an owner; each record type then adds the fields that give it meaning.
EvidenceRef:
  source_system, source_record_id, source_revision, owner
  valid_from, valid_to, recorded_from, recorded_to

RoleAssignment:
  person_id, role_id, entity_id, evidence_ref
AuthorityGrant:
  grant_id, subject_id, operation, entity_id, category
  currency, limit_minor_units, status, evidence_ref
PolicyRule:
  rule_id, policy_version, entity_id, category
  condition, exception_authority, evidence_ref
OperationalFact:
  subject_id, fact_type, value, unit, evidence_ref
DecisionRecord:
  decision_id, request_id, disposition, approver_id
  reason, evidence_refs, outcome_ref, access_classification
Dependency:
  dependent_id, prerequisite_id, condition
  severity, resolution_owner, waiver_rule, evidence_ref
Money is stored in minor units with a currency, so USD 48,000 becomes 4800000 cents. An amount without its unit can pass a syntactic schema and still be wrong by a factor of one hundred. Foreign-currency conversion would require its own approved rate, time and policy; the example avoids that additional problem.
Keep role assignment separate from authority. A person can hold a role while a grant is suspended; a service identity can have a limited operational capability without becoming the human approver. A dependency can point to a review decision without implying that every prior decision authorizes future work.
The model also needs completeness. If a required source cannot establish whether there are active supplier holds, an empty list should not mean “no holds.” Return a coverage status for the lookup. A known active hold can block creation while another unavailable source leaves the complete recommendation incomplete. Do not force all evidence into one boolean.
Define terms before importing an ontology
An ontology project begins with disagreements about meaning, not a file format. Does “owner” mean accountable executive, service operator, data steward or record author? Does an approval limit apply to the incremental spend, total contract value or outstanding exposure? For the fictional purchase, define the amount basis in the rule rather than leave the model to infer it.
Maintain a small glossary with definitions, identifiers, permitted values, source mappings and examples. Map supplier_status=H in one application to its documented meaning; do not infer a hold from an unexplained letter. Preserve an explicit unresolved mapping when source owners disagree.
SKOS is useful for controlled concepts, labels and mappings. OWL 2 offers a more formal vocabulary for ontologies. Choose the needed expressiveness: a shared category list does not require a full inference system, and a semantic relationship is not automatically a business permission.
Domain models can reduce reinvention. FIBO describes financial concepts and relationships; the Common Core Ontologies offer a broader ontology suite. Neither supplies an organization’s current approval grants or local exception policy. Adopt a selected vocabulary only where its meaning fits, record the version and extensions, and test the mappings with domain owners.
Provenance deserves the same care. W3C PROV provides a family of specifications for describing provenance. An application can use a smaller evidence model, but should still distinguish the original source, the transformation that produced a derived record and the actor responsible for it. An extracted policy condition and the approved source passage should not become indistinguishable copies.
The twin may materialize selected records or query the sources when needed. Materialization can reduce repeated joins and support historical queries, but creates synchronization, retention and access work. Virtual queries reduce copying while depending on source availability and latency. A hybrid can retain identifiers and history while obtaining a consequential current status from its owning application.
Preserve when a fact applied and when you learned it
Two times can matter for the same record. A delegation may expire on Friday, while the integration learns about the expiry on Monday. The business-effective period and the time the system observed or recorded the fact answer different questions.
For current decisions, establish the effective state required by the action and whether your knowledge of that state is fresh enough. For historical analysis, preserve enough source-version history to reconstruct what was known when the earlier recommendation was made. The requirements for reconstructing the legally effective state may be different; define them with the responsible business and records owners.
Useful fields include a source record identifier, source version, valid-from and valid-to values where relevant, observation time, ingestion time, and provenance. A correction should preserve the history needed for the task rather than quietly overwriting every trace of the earlier value.
Neo4j’s temporal values documentation describes temporal data types available to Cypher. Those types help represent time. Application logic still has to define validity, resolve conflicting sources, select the relevant version, and decide which changes require a new approval. A date property does not provide those semantics automatically.
Event-driven updates can reduce delay, but an event stream is another dependency to operate. Handle repeated and out-of-order events, source revisions, ingestion failures, and gaps discovered during reconciliation. Keep a recovery path to the authoritative source. An event timestamp alone is not sufficient evidence that no later update was missed.
A backdated hold changes two different histories
Suppose supplier snapshot revision 6 says clear at 09:00 UTC. Revision 7 establishes a hold effective at 10:00, but the integration receives it at 10:06. A recommendation made at 10:03 used the best record the integration had, while the business-effective state was already different. Those facts should both remain recoverable.
| Time | Event | Required interpretation |
|---|---|---|
| 09:00 | Revision 6 received, supplier clear | A known state with a source revision, not a guarantee about future changes |
| 10:00 | Hold becomes effective at source | Business-effective start of the hold |
| 10:03 | Cached context is used | Preserve that revision 6 was the observed evidence; do not rewrite the old log |
| 10:06 | Revision 7 arrives | Update current knowledge and identify affected pending recommendations |
| 10:30 | Hold is cleared in revision 8 | A later business state, not proof there was never a hold |
| 10:32 | A delayed copy of revision 7 arrives | Return duplicate, retaining its first recorded arrival and leaving current state at revision 8 |
The source event below is an application-specific full snapshot. Its revision is ordered only within this source record; it is not a universal sequence number. The consumer assigns its own recording time.
{
  "source_system": "supplier_registry",
  "source_record_id": "example-supplier-03",
  "revision": 7,
  "valid_from": "2026-10-18T10:00:00Z",
  "valid_to": null,
  "status": "hold",
  "reason_code": "review_required"
}
This small Python example demonstrates duplicate handling, conflicting same-revision detection and preservation of a late snapshot. It is a local teaching example, not a durable ingestion service or a complete bitemporal query engine. The source is assumed to issue trustworthy, monotonically increasing integer revisions for complete snapshots of a record. Partial patches or unordered revision identifiers need a different reducer.
from copy import deepcopy

def ingest_snapshot(history, current, event, recorded_at):
    key = (event["source_system"], event["source_record_id"])
    version_key = (*key, event["revision"])
    existing = history.get(version_key)
    if existing is not None:
        if existing["snapshot"] != event:
            raise ValueError("conflicting snapshot for the same revision")
        return "duplicate"

    history[version_key] = {
        "snapshot": deepcopy(event), "recorded_at": recorded_at
    }
    previous = current.get(key)
    if previous is None or event["revision"] > previous["revision"]:
        current[key] = deepcopy(event)
        return "current_updated"
    return "late_snapshot_archived"
The repeated delivery of revision 7 at 10:32 returns duplicate. If an unseen older revision first arrives after revision 8, the function records it and returns late_snapshot_archived.
The current pointer chooses the newest known source revision, rather than the state effective at every action time. If a release effective at 10:30 arrives at 10:20, an execution check must still select the state applicable at 10:20; the future release cannot clear the hold early. A full temporal model also needs rules for effective intervals, corrections, withdrawals and which version was known at a specified time. Retain the original snapshots so those rules can be applied without inventing history from today’s value.
Production ingestion additionally needs authenticated producers, schema validation, durable atomic writes, replay, deletion handling, conflict quarantine and a way to detect missing changes. A full snapshot can supersede an earlier snapshot for current-state purposes, but gaps may still matter to history. A revision jump should not silently certify a complete event history.
Reconciliation is the independent recovery path. Compare the maintained projection with an authoritative snapshot or supported change cursor, report discrepancies and repair them under the source contract. An event consumer being online does not establish that it has received every relevant change.
| Source | Useful update pattern | Reconciliation question | On unavailable or stale evidence |
|---|---|---|---|
| Authority register | Grants, revisions and revocations | Does the projection match the source’s active grants? | Do not authorize from an unbounded old grant |
| Policy publisher | Approved publication and effective-date changes | Are drafts, withdrawals and future rules represented correctly? | Return unresolved applicability |
| Supplier system | Status changes plus execution-time lookup | Are active holds and releases complete? | Block or use the process owner’s explicit review path |
| Budget service | Transactional reservations | Does available capacity include outstanding reservations? | Do not substitute a copied balance for reservation |
| Decision archive | Approved records and outcome updates | Are exceptions and abandoned proposals distinguished? | Omit unavailable precedent without inventing it |
The response to a missing precedent can be less restrictive than the response to unknown authority. Freshness and failure behavior follow the decision consequence; there is no universal four-hour tolerance for every source.
Choose retrieval from the questions it must answer
Use document retrieval for the relevant policy explanation, structured queries for exact records, and business APIs for authoritative operational checks. A knowledge graph becomes useful when relationships and traversals are central to the questions, such as resolving delegated responsibility across several scopes. A vector index can help find related material; enforce access through the application’s authorization checks independently of similarity.
Before choosing a platform, write representative queries and the expected evidence. For example: resolve the valid grant for this requester and order scope; explain the applicable purchasing rule; identify the source and time of the supplier hold; retrieve comparable exceptions the reviewer is permitted to see. These queries exercise different capabilities.
A hybrid retrieval path needs to preserve access restrictions through every stage. Filtering the text shown to the model is insufficient if a prior stage exposes restricted titles, counts, snippets, or identifiers to an unauthorized user. Evaluate the full retrieval path, including caches and derived indexes, against the intended information boundary.
Keep query construction under application control. Validate identifiers and allowed operations, use parameterized queries where supported, and expose bounded business capabilities rather than unrestricted database access. The model can propose an operation; it should not be able to manufacture a new privilege by changing a query or adding an identity field.
I would compare platform options using the actual workload: relationship queries, temporal requirements, access controls, update and reconciliation behavior, operational skills, portability, and cost. A familiar relational platform with reliable business APIs can be a better starting point than introducing a graph the team cannot maintain. A graph earns its place when the relationship queries and their operating requirements justify the additional platform.
Follow one relationship query before adding semantic search
A purchasing context service might first resolve an order to its entity, category, amount and supplier. It then asks for grants that cover that exact operation and scope at the effective time. Only after the caller’s access is established should it assemble related policy explanations or comparable decisions.
The following parameterized SQL fragment makes the two time dimensions explicit. It is query syntax for an illustrative authority_grant_version relation, not a complete authorization implementation. The authenticated principal and order facts must be supplied by trusted application code, rather than copied from a model’s request. A missing result is not an allow decision, and a matching grant still leaves other action conditions to check.
SELECT grant_id, source_revision, policy_version, limit_minor_units
FROM authority_grant_version
WHERE subject_id = :authenticated_principal
  AND entity_id = :order_entity
  AND category = :order_category
  AND operation = :operation
  AND currency = :order_currency
  AND limit_minor_units >= :order_amount_minor_units
  AND status = 'active'
  AND valid_from <= :effective_at
  AND (valid_to IS NULL OR :effective_at < valid_to)
  AND recorded_from <= :known_at
  AND (recorded_to IS NULL OR :known_at < recorded_to);
The intervals are half-open: an end time is excluded. In this simplified example, timestamps use one canonical UTC representation and precision. SQLite compares these TEXT values lexically: 10:00:00.000Z can sort before 10:00:00Z even though they represent the same instant. The fixture below rejects non-canonical stored values and query inputs before comparing them. A real database should use appropriate temporal types and define timezone conversion and boundary behavior. Resolve overlapping active versions through the source’s explicit rule, or return an incomplete/conflict result.
To exercise those predicates locally, save the preceding query as grant-query.sql and run this Python 3 fixture in the same directory. This independent predicate fixture sets expiry to 10:00 UTC on 18 October so the exact boundary can be tested; the purchasing narrative’s Friday expiry is a separate illustrative record. It uses the standard-library SQLite driver and fictional records, with no service connection. It checks selection behavior, not database row-security policies or a complete authorization service. The named-parameter syntax is supported by this driver; use the binding mechanism of your actual database client when adapting it.
from pathlib import Path
from datetime import datetime
import sqlite3

def canonical_utc(value):
    pattern = "%Y-%m-%dT%H:%M:%SZ"
    parsed = datetime.strptime(value, pattern)
    if parsed.strftime(pattern) != value:
        raise ValueError("timestamp must use canonical UTC seconds")
    return value

db = sqlite3.connect(":memory:")
db.execute("""CREATE TABLE authority_grant_version (
    grant_id TEXT, source_revision INTEGER, policy_version TEXT,
    limit_minor_units INTEGER, subject_id TEXT, entity_id TEXT,
    category TEXT, operation TEXT, currency TEXT, status TEXT,
    valid_from TEXT, valid_to TEXT, recorded_from TEXT, recorded_to TEXT
)""")
db.execute("INSERT INTO authority_grant_version VALUES (?,?,?,?,?,?,?,?,?,?,?,?,?,?)", (
    "g1", 7, "p2", 5000000, "u1", "e1", "equipment", "create_order",
    "USD", "active", "2026-10-17T00:00:00Z", "2026-10-18T10:00:00Z",
    "2026-10-17T09:00:00Z", None
))
for row in db.execute("SELECT valid_from, valid_to, recorded_from, recorded_to "
                      "FROM authority_grant_version"):
    for value in row:
        if value is not None:
            canonical_utc(value)
query = Path("grant-query.sql").read_text()

def select_grants(values):
    checked = dict(values)
    for field in ("effective_at", "known_at"):
        checked[field] = canonical_utc(checked[field])
    return db.execute(query, checked).fetchall()

args = dict(
    authenticated_principal="u1", order_entity="e1",
    order_category="equipment", operation="create_order",
    order_currency="USD", order_amount_minor_units=4800000,
    effective_at="2026-10-18T09:59:59Z", known_at="2026-10-18T09:59:59Z"
)
assert len(select_grants(args)) == 1
for field, value in [
    ("effective_at", "2026-10-18T10:00:00Z"),
    ("known_at", "2026-10-17T08:59:59Z"),
    ("authenticated_principal", "u2"), ("order_entity", "e2"),
    ("order_category", "services"), ("operation", "pay"),
    ("order_currency", "EUR"), ("order_amount_minor_units", 5000001)
]:
    assert select_grants(dict(args, **{field: value})) == [], field
for field in ("effective_at", "known_at"):
    for value in ("2026-10-18T10:00:00.000Z", "2026-10-18T06:00:00-04:00"):
        try:
            select_grants(dict(args, **{field: value}))
        except ValueError:
            pass
        else:
            raise AssertionError("non-canonical timestamp was accepted")
db.execute("UPDATE authority_grant_version SET status = 'revoked'")
assert select_grants(args) == []
print("Grant predicate checks passed")
The fixture is deliberately small enough to inspect. Add overlapping versions, conflicting source owners and missing coverage before treating it as an application test set. The supplier hold and budget reservation are absent from this relation, so a selected grant is only one input to the purchase decision.
A graph can express the corresponding relationship traversal directly. This Cypher is illustrative and was not executed against a live Neo4j database:
MATCH (p:Person {id: $authenticatedPrincipal})-[:RECEIVES]->(g:AuthorityGrant)
WHERE g.entityId = $orderEntity
  AND g.operation = $operation
  AND g.category = $orderCategory
  AND g.currency = $orderCurrency
  AND g.limitMinorUnits >= $amountMinorUnits
  AND g.status = 'active'
  AND g.validFrom <= datetime($effectiveAt)
  AND (g.validTo IS NULL OR datetime($effectiveAt) < g.validTo)
RETURN g.id, g.sourceRevision, g.policyVersion
This graph fragment deliberately shows only business validity. A historical implementation would also apply recording-time selection and version-resolution rules. Neither query establishes producer trust, completeness, caller access to the order, or permission to disclose every returned property. Those checks belong in the service around the query.
Semantic retrieval can then search within the set of records the caller may access and that apply to the question. Resolve authorization and applicability before returning titles, counts or snippets to the caller. If the chosen search engine cannot enforce the required restriction during retrieval, redesign the path; filtering only the final generated paragraph is too late.
Select platforms by a capability you can test
The table describes architecture options, not a market ranking. Product capabilities were checked against linked official documentation in October 2026; editions and deployed configurations still need validation.
| Option and primary documentation | Useful role | Question to prove in a prototype |
|---|---|---|
| Relational database and business APIs; PostgreSQL 18 row security | Exact records, joins and database-enforced row restrictions | Do owner/service roles bypass intended restrictions, and can the required transaction boundary be enforced? |
| Property graph; Neo4j temporal values and vector indexes | Relationship traversal and selected similarity search | Do time/version semantics, access and vector-query behavior work for the actual workload? |
| Search index; OpenSearch document-level security | Search over permitted documents | Are restrictions consistent across queries, aggregations and the credentials used by the application? |
| RDF/ontology tooling using OWL 2 | Explicit shared semantics and selected inference | Is the formal model needed, and can operators explain and maintain its conclusions? |
| Existing metadata catalog | Source discovery, ownership and lineage | Does it identify the source, or does it actually supply the current business fact and execution control? |
PostgreSQL’s documentation notes important row-security exceptions, including table-owner and privileged-role behavior. A restricted end-user policy can be defeated by connecting every request through an unrestricted application role. Test the deployed identity path, not just the policy definition.
A metadata catalog can be valuable without becoming the authority service. An enterprise search product can find a policy without owning its approval. A managed graph still leaves data modeling, mappings, updates and incident response with someone. Procurement should ask for evidence of the needed functions, export paths, edition constraints and operating responsibilities rather than an “AI-ready” label or an unverified market-share claim.
Keep identity and permission attached to the operation
Role-based controls, attribute-based rules, and relationship checks can all be useful. A purchasing role may permit entry to the workflow, while the order amount, entity, delegation period, and supplier status determine whether a specific action is allowed. The right combination depends on the application and the organization’s policy.
NIST’s ABAC guide describes authorization based on attributes of subjects, objects, operations, and sometimes environmental conditions evaluated against policy. It supplies useful terminology for examining such decisions. It does not mean every enterprise should replace all role-based access with a new attribute system.
Resolve the caller’s identity from the trusted authentication context. Keep it separate from a person or order named as the target of a query. A tool argument such as requester_id is untrusted input unless the application validates its relationship to the authenticated caller. A valid service credential also does not establish that its holder may act for every user or access every record.
The application must define how delegation works across the request chain, including the service’s own permitted operations. Check what the destination actually receives and enforces. Do not assume that forwarding a person’s name or copying a token into a tool argument provides secure identity propagation.
Access rules need negative examples
The examples below are proposed application rules, not a universal enterprise policy. They combine roles, trusted attributes and explicit relationships. NIST’s ABAC terminology helps describe this approach, but does not make it superior to every role-based design.
| Context | Illustrative rule | Denied-case test |
|---|---|---|
| Organizational hierarchy | A manager can view permitted team staffing summaries | A manager cannot use that edge to inspect another entity’s payroll |
| Project work | Membership and classification permit access to selected project records | A project ID in the prompt does not establish membership |
| Customer account | Assignment and task purpose permit a defined case operation | A handler cannot adopt another handler’s assignment by naming them |
| Purchasing authority | Active scoped grant plus current action conditions permit creation | An executive title alone cannot bypass a hold or grant limit |
| Service-to-service call | Service capability is constrained to the delegated business operation | A valid service token cannot query arbitrary principals |
An asserted purpose such as “audit” is not evidence of authorization. Resolve allowed purpose from an established workflow or another trusted context, and limit it to the requested operation. If users can freely type the attribute that grants access, the policy is only a form field.
Test summaries, embeddings and caches too. A user removed from a project should not retain access through a cached context package generated under old membership. Scope cache keys and invalidation to relevant identity and policy state; avoid sharing results across callers merely because their text queries match.
Use MCP as an interface boundary
MCP can expose the context lookup or other bounded capabilities to compatible clients. Keep the protocol role distinct from the business rule. The current MCP article explains revision compatibility, transports, authorization, and tool boundaries in more detail.
An application-specific lookup might accept an order identifier and a requested operation. The service would obtain the verified caller context separately, validate the operation, perform the permitted checks, and return the result the caller is allowed to receive. Do not let the model supply an arbitrary principal whose permissions the service then adopts.
This illustrative response deliberately returns a blocked decision rather than an approval inferred from the amount. It is an application payload, not a complete MCP message:
{
  "order_id": "example-po-014",
  "operation": "create_order",
  "decision": "blocked",
  "reasons": ["delegation_expired", "supplier_hold_active"],
  "facts_checked_at": "2026-10-18T10:06:30Z",
  "source_refs": [
    {"system": "authority_register", "record": "example-grant-09", "version": "7"},
    {"system": "supplier_registry", "record": "example-supplier-03", "version": "7"}
  ],
  "next_step": "resolve_hold_and_request_current_approver"
}
The response should explain uncertainty and source availability as well as the nominal result. If the authority service cannot be reached, do not turn an incomplete lookup into has_authority: true. Use a state whose meaning the consuming application understands and whose behavior has been tested.
The MCP security guidance explicitly addresses risks such as token passthrough. Validate credentials for the service and purpose that receives them; do not treat a token obtained for another destination as a universal forwarding mechanism. Business-level delegation and approval still need their own supported design.
Expose a small tool contract, not an arbitrary principal query
The MCP tools specification, revision 2026-07-28, describes tool input schemas and structured results. The following application example uses that interface shape. Its fields and decision vocabulary are this workflow’s design, not an EDT extension standardized by MCP.
{
  "name": "get_purchase_context",
  "description": "Read the permitted decision context for one purchase order.",
  "inputSchema": {
    "type": "object",
    "properties": {
      "order_id": {"type": "string", "minLength": 1},
      "operation": {"type": "string", "enum": ["create_order"]}
    },
    "required": ["order_id", "operation"],
    "additionalProperties": false
  },
  "annotations": {"readOnlyHint": true}
}
There is no person_id that tells the service whose powers to adopt. The service resolves its authenticated caller, verifies access to the order, reads the amount and entity from that order, and applies the source contracts. A separate audited capability would be needed to inspect another person’s grants for an authorized administrative purpose.
{
  "jsonrpc": "2.0",
  "id": 14,
  "method": "tools/call",
  "params": {
    "name": "get_purchase_context",
    "arguments": {
      "order_id": "example-po-014",
      "operation": "create_order"
    }
  }
}
This is an abbreviated tools/call fragment. Actual requests in revision 2026-07-28 must include params._meta fields for io.modelcontextprotocol/protocolVersion and io.modelcontextprotocol/clientCapabilities; clientInfo is recommended. The base protocol's per-request field table gives the requirements. A complete successful result also includes resultType: "complete".
For an authorized caller, the blocked business payload above can be returned as structured content, with serialized JSON in a text block as recommended by the tools specification. Here the context lookup succeeded and found a block, so its tool result uses isError: false; it has not attempted and failed to create the order. A failed tool execution uses isError: true, while malformed protocol requests have a separate error mechanism. A denied caller should receive the service’s permitted error response without leaking whether a sensitive order exists. Declare and validate a complete output schema when clients depend on the response structure.
The read-only annotation describes intent; it is not an access control. The implementation must prevent writes. Similarly, an eligible_for_review or ready result must not be interpreted as a transferable credential to create an order later. A separate write capability needs its own scoped authorization, approval and destination checks.
Treat retrieved content as evidence, not instructions
A policy document, email, website, or tool result can contain text that tries to redirect an agent. Keeping the data inside an enterprise system does not make every sentence trustworthy as an instruction. Preserve the boundary between governing instructions, a user’s authorized request, and material retrieved for reference.
OWASP’s prompt-injection prevention guidance recommends layered defenses and constrained privileges; model-based guardrails are only one layer. In this architecture, validate inputs and outputs at the application boundary, constrain the available actions, protect credentials, and enforce the destination’s permissions independently of a model’s interpretation.
Test a malicious supplier note that asks the agent to ignore the hold, reveal unrelated records, or send information elsewhere. The relevant result is whether restricted data or actions become available through the complete path. A reassuring refusal in the chat window would not be enough if the tool had already performed the operation.
The context layer itself also needs protection. Control who can change a delegation, publish a policy version, or correct a source record. Separate a proposed update from an approved authoritative change, and make consequential corrections traceable. Otherwise, an attacker may alter the facts the model faithfully follows.
Recheck at execution and reconcile the result
An approval can be valid when issued and insufficient for a later action if material conditions change. Define which changes invalidate it. For the purchasing case, a new supplier hold, a changed order amount, or a revoked grant can require another check before creation.
The destination should enforce the conditions that need to hold when the action is committed. Where the system supports transactional checks or version preconditions, use them deliberately. If it does not, document the remaining race window and decide whether the action needs human handling or a different integration. A prior read and a later write are not automatically one transaction.
Also design for a request that times out after reaching the destination. It may have succeeded even though the agent did not receive the result. Use the destination’s supported idempotency or correlation mechanism when available, and reconcile uncertain outcomes before retrying. Cancellation of a client request does not establish that downstream work was undone.
Retain the evidence needed to investigate the decision: intended operation, responsible identities, relevant source references and versions, approval, destination result, and any recovery action. Choose redaction, access, and retention rules for those records. Copying every prompt, source document, and credential-bearing response into a broad log would create an avoidable exposure.
A conditional write protects only the state it covers
Suppose the order service returns order representation ETag "order-v12". A client later submits a supported update with that tag:
PATCH /orders/example-po-014
If-Match: "order-v12"
Content-Type: application/merge-patch+json

{"requested_state":"approved","approval_ref":"example-approval-07"}
HTTP semantics for If-Match define a conditional request using the resource’s entity tag. If that representation changed, the server can reject the operation rather than overwrite the change. The partial update uses JSON Merge Patch, rather than a PUT replacing the complete order representation. The example is an interface sketch; the actual destination must support these semantics.
An order ETag does not automatically cover a supplier hold maintained in another service. The destination must define which authorization, hold and reservation checks occur with the committed state transition. Transaction isolation helps within a participating database, but does not create an atomic transaction across every remote service. PostgreSQL's isolation documentation is useful background for choosing and testing local behavior, including retry requirements.
Where a distributed check cannot be made atomic, name the remaining race window and its consequence. For some work, an explicit reservation or short-lived authorization bound to material values can help. Other actions require a different integration or human handling. Do not silently present an advisory context lookup as a transaction guarantee.
For uncertain results, retain an operation identifier before submission. Use the destination’s supported idempotency mechanism, whose retention period and payload-mismatch behavior must be known. An arbitrary header called Idempotency-Key does nothing unless the destination implements it. After a timeout, query the existing operation or transaction state before deciding whether to retry.
| Destination observation | Workflow state | Next action |
|---|---|---|
| Explicit business rejection | Rejected | Preserve the reason and permitted review path |
| Accepted for asynchronous processing | Pending | Poll or receive the supported completion event |
| Confirmed committed result | Completed | Retain the destination identifier and material result |
| Timeout after submission | Unknown | Reconcile using the operation identifier |
| Duplicate submission recognized | Existing operation | Return or reconcile the original result |
| Conflicting payload under reused identifier | Conflict | Stop; do not turn it into another transaction |
Transport success, business eligibility and completed action are different observations. They should remain different in structured status fields, monitoring and the message shown to a person.
Test the failure paths before expanding access
Build a small evaluation set with the business owner and application team. Each case needs an expected decision, evidence that must be present, actions that must remain unavailable, and a way to verify the destination result. Keep model quality, application enforcement, and end-to-end operation as distinct checks.
| Test case | Required behavior |
|---|---|
| Expired or revoked grant | Do not approve from the older limit; identify the permitted review path. |
| Wrong entity or spending scope | Reject the otherwise valid grant for this order. |
| Active supplier hold | Block creation at the required control boundary. |
| Authority source unavailable | Return the defined incomplete/review state, without widening access. |
| Out-of-order or missed update | Detect stale state through revision handling or reconciliation. |
| Malicious retrieved instruction | Keep unrelated data and actions unavailable. |
| Revocation after recommendation | Recheck before committing the operation. |
| Timeout after destination acceptance | Reconcile the existing operation before a retry can duplicate it. |
Use realistic cases without placing live personal or confidential client records into test fixtures unnecessarily. Include difficult but legitimate requests, because a control that rejects all work can appear safe while making the workflow unusable.
For the model’s contribution, assess whether its explanation reflects the evidence, states what is missing, and helps the responsible person take the next step. For the workflow, measure accepted outcomes, review effort, waiting time, corrections, control failures, and complete operating cost. Keep the baseline and acceptance thresholds attached to the same workload.
Transfer the design across industries deliberately
These are hypothetical application choices, not evidence that a particular sector deployment has passed review. They help identify which layer deserves the most attention.
| Decision | Decisive context | Implementation question |
|---|---|---|
| Commercial-credit package | Total facility, scoped authority, exposure, exception and committee capacity | Is the decision using total exposure rather than only the increase, and are pending commitments included? |
| Hospital procedure scheduling | Facility privileges, prerequisites, resource availability and current assignment | Does a proposed slot remain conditional on the authoritative scheduling and clinical processes? |
| Insurance claim routing | Contract/event version, assignment, case status and permitted precedent | Can the handler see this case and distinguish applicable terms from today’s procedure? |
| Project staffing | Skills, allocations, prerequisites and transfer dependencies | Does a matching profile have capacity and the required approvals for the period? |
Healthcare context requires its own access, privacy and clinical-governance assessment; this guide does not derive treatment authority from a graph. Insurance and lending likewise need the actual contract and jurisdictional requirements. Use the model to discover those dependencies rather than claim that the model certifies compliance.
Expand through evidence gates
Begin in a read-only path that lets the team inspect sources, permissions, and freshness without creating orders. Compare its recommendations with the current process and resolve disagreements. A demonstration that returns the expected answer once is not enough to move into action.
Next, place the context in a human-reviewed workflow. Check whether the evidence actually helps the reviewer, whether the proposed escalation goes to the right person, and whether changing conditions are visible. Use the results to revise the source contracts and interface before adding write access.
Bounded actions come after the destination controls, approvals, uncertain-result handling, monitoring, and rollback or recovery procedures have been exercised. Define who can stop the integration and how pending work will be reconciled. The business owner should accept the remaining limitations alongside the measured benefits.
Estimate scope and staffing after examining the systems involved, including the work of obtaining access, resolving ownership, repairing source data, and operating the integration. A narrow workflow may move quickly, while a poorly governed source can hold the whole design back. The team should know which dependency is setting the pace before committing to a rollout date.
Federation across departments or organizations is a further choice, not the required destination of every pilot. It adds independent policies, source contracts, identity boundaries, data-sharing permissions, and failure ownership. Agree on meanings and permitted operations before connecting more systems. A shared vocabulary or protocol cannot supply a missing agreement about what may be disclosed or done.
Plan five increments around outcomes, not calendar promises
The five context layers do not require a five-stage waterfall. A supplier hold may need to enter the first purchasing prototype, even before a complete organizational topology exists. The increments below are a planning aid; sequence them according to the decisive facts and available source contracts.
| Increment | Concrete deliverable | Evidence needed to expand |
|---|---|---|
| Identify one decision and its owners | Context contract, source map, identifiers and baseline cases | Owners agree which facts change the result and what incomplete means |
| Build read-only context | Five-layer minimum model, mappings, permission-aware queries | Expected records, wrong-scope exclusions and provenance match the source |
| Operate the time model | Update handlers, replay, backdated correction and reconciliation | Duplicate, late, missing and conflicting updates have observable handling |
| Add reviewed decisions and bounded action | Review packet, scoped write interface and destination reconciliation | Revocation/race/timeout tests pass for the chosen action; stop/recovery owner exists |
| Reuse and extend | Second workflow, comparable cost/quality measures and reusable contracts | Reuse is demonstrated without importing inappropriate permissions or semantics |
Each increment needs a tangible reader-visible result. A first review packet might show why the purchase is blocked and which records support that result. The next iteration might route the exception correctly. Only a later one may create an order under supported controls. Judge the graph by the accepted decisions it helps produce and the work required to maintain it.
Budget for access approvals, unresolved identifiers and source repair before promising a schedule. The hardest dependency may be a policy owner deciding which exceptions exist, rather than the query engine. A stalled source agreement should be visible in the plan instead of hidden behind a completed ingestion task.
Use maturity as a diagnostic, not a score to advertise
This seven-stage rubric is my planning aid, not a validated industry maturity scale. An organization may be advanced for one workflow and unable to support another. Evaluate the weakest required capability for the decision rather than average away a missing control.
| Stage | What is demonstrable | Next useful question |
|---|---|---|
| 0: Decision not mapped | No agreed source-to-decision record | Which facts and owners determine one outcome? |
| 1: Sources identified | Stable identifiers and named authoritative sources | Can permitted users retrieve the correct records? |
| 2: Applicable context assembled | Scope, rule versions, grants and dependencies connect | What happens when a required fact is missing or contradictory? |
| 3: Change is operated | Effective/recorded time, replay and reconciliation are tested | Can an old decision be reconstructed without rewriting its evidence? |
| 4: Reviewed workflow | Evidence helps accountable reviewers make and investigate decisions | Does it improve accepted outcomes and review effort? |
| 5: Bounded execution | Destination enforcement and uncertain-result recovery are exercised | Which second workflow can reuse the capability safely? |
| 6: Governed reuse or federation | Contracts, identity, disclosure and operating ownership span domains | Does the added reach justify its semantic and maintenance cost? |
A read-only research workflow can be valuable at stage 4 without ever executing transactions, and strong internal reuse does not create a need for federation. The appropriate stopping point follows the work’s requirements. Node count and autonomous learning are poor substitutes for the capabilities in this rubric.
Operate the representation after the launch
Failures are often visible as ordinary symptoms before anyone calls them an architecture problem. A context service that repeatedly returns the wrong approver may have a stale grant projection, an identifier mismatch or the wrong amount basis. Adding a larger model does not distinguish those explanations.
| Symptom | Investigate | Bounded response |
|---|---|---|
| Relevant passage, wrong decision | Scope, effective time and rule interpretation | Reconstruct the exact record/version path |
| Same source revision, different value | Producer defect or tampering | Quarantine conflict; do not accept latest arrival blindly |
| Projection lags while consumer appears healthy | Source cursor, dead-letter queue, replay gap | Reconcile with authoritative state |
| Graph has many entities but few consumers | Real query and workflow requirements | Narrow the model to a useful decision |
| Every incomplete input blocks harmless research | Failure policy mismatched to consequence | Separate advisory gaps from action prerequisites |
| Privileged service returns cross-entity results | Credential scope and query/access enforcement | Contain access and retest negative cases |
| Approvals repeatedly become stale | Material changes and validity duration | Reassess the approval/check boundary |
| Timeouts create duplicate work | Correlation, idempotency and reconciliation | Resolve the original attempt before resubmission |
“Imperfect data is better than none” depends on use. A partially known skills profile may help identify an expert. Incomplete authority evidence cannot grant a payment power. Define missing, contradictory, stale and unavailable states separately so that recovery can be proportionate.
The operating record should connect request, permitted caller, source versions, retrieval, evaluation, approval and destination result. Record stage timing and dependency errors so a slow source can be distinguished from generation delay. Measure p50/p95 or other useful latency distributions by operation and include unresolved outcomes, rather than average only successful fast calls.
Minimize sensitive content in logs. Source identifiers and selected evidence may suffice; raw documents, credentials and unrestricted prompts often do not belong in a shared trace. Access, retention, correction and legal-hold decisions need accountable owners. A hash can help detect a changed artifact, but does not establish its truth or the authority of whoever supplied it.
Run a recurring reconstruction exercise: choose an accepted decision, recover the versions known at that time, explain its authority and constraints, and reconcile the destination result. Include a corrected or disputed case. That exercise tests whether the record supports the operating job better than a dashboard count of ingested entities.
Federation begins with a disclosure agreement
Cross-organization context can be useful in a supply chain. A manufacturer may need to know whether a supplier can meet a delivery commitment without needing its employee roster or entire production schedule. Exposing a bounded answer can be more appropriate than sharing a graph.
Federation therefore starts with a question and a contract: which organization owns the fact, what the recipient may use it for, which identities may request it, what time and units mean, how corrections propagate, and who handles an outage or disputed assertion. Internal data-product ownership is a useful organizing analogy, but independent organizations still need explicit agreements.
{
  "contract": "example-delivery-capacity-v1",
  "issuer": "example-supplier",
  "audience": "example-manufacturer",
  "subject": "example-po-014",
  "permitted_purpose": "delivery_planning",
  "assertion": "capacity_review_required",
  "valid_until": "2026-10-19T12:00:00Z",
  "source_revision": "example-revision-08",
  "correction_channel": "contract-defined-interface"
}
This illustrative payload would need a defined trust mechanism before use: naming an issuer or audience does not authenticate either one. The production contract must establish authenticity, permitted recipients, replay/expiry behavior and a working correction interface. It should also say whether an assertion such as “capacity available” is advisory or a binding commitment; the destination process must support that meaning.
Federation can use domain APIs, permitted queries or selected replicated records. Virtualization does not prevent the receiving application from logging or retaining returned information. Embeddings can also encode sensitive relationships; sharing them is not an automatic privacy or sovereignty solution. Assess the data actually disclosed, including derived facts.
Readiness means that each participant can maintain identifiers, semantic mappings, identity controls, time interpretation, source-quality commitments and a usable withdrawal/correction route. A disconnected partner must not quietly become evidence that no constraint exists. Return the agreed unavailable state and use the business fallback.
The purchasing workflow may never need federation. Internal reuse can deliver sufficient value with far fewer parties and contracts. Add the boundary only when a real decision needs information owned outside it, and when those owners can sustain the agreement.
Keep the operating cost visible
The work continues after the first integration. Policies change, grants expire, source APIs evolve, and people challenge decisions. Assign ownership for those changes and budget for reconciliation, access reviews, evaluation, incident handling, and the underlying platforms.
My preference is to expand only where another source or relationship changes a decision worth improving. That keeps the architecture accountable to the work. If maintaining the context costs more than the rework it removes, narrow it or use the existing application more directly.
Use the Version Drift framework to examine changes between evidence and action, and Decision Velocity to define a better accepted outcome. The AI economics workbook helps make the cost boundary explicit. These tools are most useful when filled in for the same workflow and reviewed by the people who will operate it.
Discover more from Ajith Vallath Prabhakar
Subscribe to get the latest posts sent to your email.
One Comment